

Real Palo Alto Networks PCNSA Exam Questions [Updated 2024]
PCNSA Exam Dumps Pass with Updated 2024 Palo Alto Networks Certified Network Security Administrator
Difficulty in writing PCNSA Exam
This exam is very difficult especially for those who have not on the job experience as a Palo Alto Certified Expert. Candidates can not pass this exam with only taking courses because courses do not provide the knowledge and skills that are necessary to pass this exam. TrainingDumps is the best platform for those who want to pass Palo Alto PCNSA with good grades in no time. TrainingDumps provides the latest Palo Alto PCNSA exam dumps that will immensely help candidates to get good grades in their final Palo Alto PCNSA exam. TrainingDumps is one of the best study sources to provide the most updated Palo Alto PCNSA Dumps with our Actual PCNSA Exam Questions PDF. Candidate can rest guaranteed that they will pass their Palo Alto PCNSA Exam on the first attempt. We will also save candidates valuable time. TrainingDumps Dumps help to pass the exam easily. Candidates can get all real questions from TrainingDumps. One of the best parts is we also provide most updated Palo Alto Certified Expert Exam study materials and we also want a candidate to be able to access study materials easily whenever they want. So, We provide all our Palo Alto PCNSA exam questions in a very common PDF format that is accessible from all devices.
NEW QUESTION # 120
An administrator manages a network with 300 addresses that require translation. The administrator configured NAT with an address pool of 240 addresses and found that connections from addresses that needed new translations were being dropped.
Which type of NAT was configured?
- A. Destination NAT
- B. Dynamic IP and Port
- C. Dynamic IP
- D. Static IP
Answer: C
Explanation:
The size of the NAT pool should be equal to the number of internal hosts that require address translations. By default, if the source address pool is larger than the NAT address pool and eventually all of the NAT addresses are allocated, new connections that need address translation are dropped. To override this default behavior, use Advanced (Dynamic IP/Port Fallback) to enable the use of DIPP addresses when necessary
NEW QUESTION # 121
Match the Palo Alto Networks Security Operating Platform architecture to its description.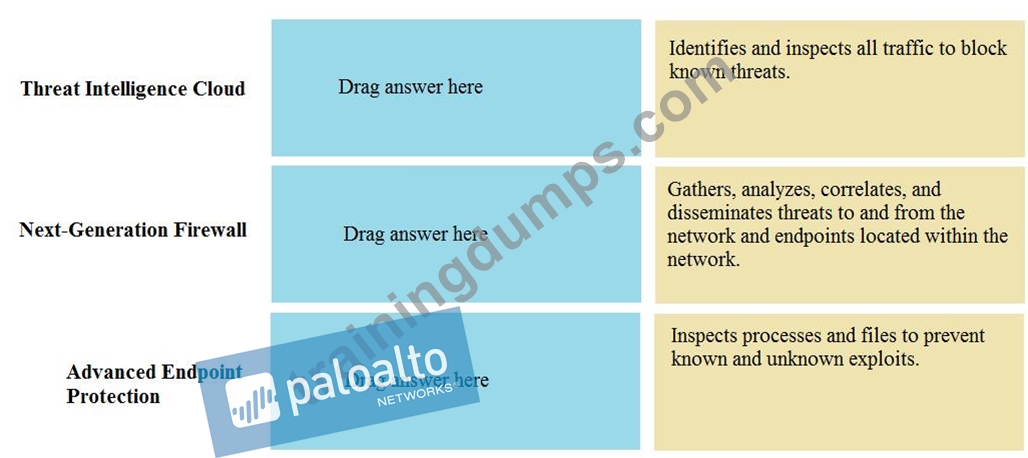
Answer:
Explanation:
NEW QUESTION # 122
An administrator is reviewing another administrator s Security policy log settings Which log setting configuration is consistent with best practices tor normal traffic?
- A. Log at Session Start and Log at Session End both disabled
- B. Log at Session Start disabled Log at Session End enabled
- C. Log at Session Start and Log at Session End both enabled
- D. Log at Session Start enabled Log at Session End disabled
Answer: B
NEW QUESTION # 123
A Security Profile can block or allow traffic at which point?
- A. before it is matched to a Security policy rule
- B. on either the data plane or the management plane
- C. after it is matched to a Security policy rule that allows traffic
- D. after it is matched to a Security policy rule that allows or blocks traffic
Answer: C
NEW QUESTION # 124
Which security policy rule would be needed to match traffic that passes between the Outside zone and Inside zone, but does not match traffic that passes within the zones?
- A. universal
- B. intrazone
- C. global
- D. interzone
Answer: D
NEW QUESTION # 125
Based on the security policy rules shown, ssh will be allowed on which port?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: B
NEW QUESTION # 126
Arrange the correct order that the URL classifications are processed within the system.
Answer:
Explanation:
Explanation
First - Block List
Second - Allow List
Third - Custom URL Categories
Fourth - External Dynamic Lists
Fifth - Downloaded PAN-DB Files
Sixth - PAN-DB Cloud
NEW QUESTION # 127
Based on the screenshot presented which column contains the link that when clicked opens a window to display all applications matched to the policy rule?
- A. Name
- B. Service
- C. Apps Seen
- D. Apps Allowed
Answer: C
NEW QUESTION # 128
A security administrator has configured App-ID updates to be automatically downloaded and installed. The company is currently using an application identified by App-ID as SuperApp_base.
On a content update notice, Palo Alto Networks is adding new app signatures labeled SuperApp_chat and SuperApp_download, which will be deployed in 30 days.
Based on the information, how is the SuperApp traffic affected after the 30 days have passed?
- A. No impact because the apps were automatically downloaded and installed
- B. No impact because the firewall automatically adds the rules to the App-ID interface
- C. All traffic matching the SuperApp_base, SuperApp_chat, and SuperApp_download is denied until the security administrator approves the applications
- D. All traffic matching the SuperApp_chat, and SuperApp_download is denied because it no longer matches the SuperApp-base application
Answer: D
Explanation:
https://docs.paloaltonetworks.com/pan-os/9-0/pan-os-admin/app-id/manage-new-app-ids-introduced-in-content-releases/review-new-app-id-impact-on-existing-policy-rules
NEW QUESTION # 129
Which two security profile types can be attached to a security policy? (Choose two.)
- A. antivirus
- B. threat
- C. vulnerability
- D. DDoS protection
Answer: A,C
Explanation:
Explanation/Reference: https://docs.paloaltonetworks.com/pan-os/8-0/pan-os-admin/policy/security-profiles
NEW QUESTION # 130
Which two configuration settings shown are not the default? (Choose two.)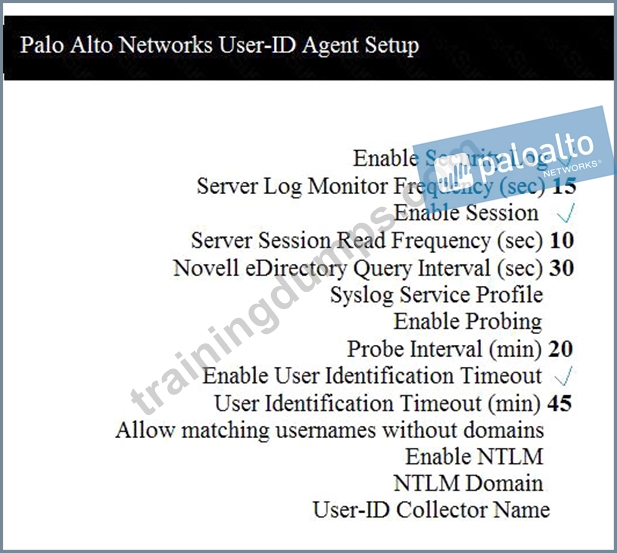
- A. Enable Security Log
- B. Server Log Monitor Frequency (sec)
- C. Enable Session
- D. Enable Probing
Answer: B,C
NEW QUESTION # 131
What are two valid selections within an Anti-Spyware profile? (Choose two.)
- A. Default
- B. Drop
- C. Deny
- D. Random early drop
Answer: A,B
NEW QUESTION # 132
Order the steps needed to create a new security zone with a Palo Alto Networks firewall.
Answer:
Explanation:
Explanation
Step 1 - Select network tab
Step 2 - Select zones from the list of available items
Step 3 - Select Add
Step 4 - Specify Zone Name
Step 5 - Specify Zone Type
Step 6 - Assign interfaces as needed
NEW QUESTION # 133
You receive notification about new malware that infects hosts through malicious files transferred by FTP.
Which Security profile detects and protects your internal networks from this threat after you update your firewall's threat signature database?
- A. Vulnerability Prote
- B. URL Filtering profile applied to inbound Security policy rules.
- C. Antivirus profile applied to inbound Security policy rules.
- D. Data Filtering profile applied to outbound Security policy rules.
Answer: C
Explanation:
ction profile applied to outbound Security policy rules.
Reference:
https://docs.paloaltonetworks.com/pan-os/9-0/pan-os-admin/policy/security-profiles
NEW QUESTION # 134
Which two components are utilized within the Single-Pass Parallel Processing architecture on a Palo Alto Networks Firewall? (Choose two.)
- A. User-ID
- B. App-ID
- C. Layer-ID
- D. QoS-ID
Answer: A,B
Explanation:
Explanation/Reference: http://www.firewall.cx/networking-topics/firewalls/palo-alto-firewalls/1152-palo-alto-firewall-single- pass-parallel-processing-hardware-architecture.html
NEW QUESTION # 135
When a security rule is configured as Intrazone, which field cannot be changed?
- A. Source Zone
- B. Destination Zone
- C. Application
- D. Actions
Answer: B
Explanation:
https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClomCAC
NEW QUESTION # 136
An administrator wishes to follow best practices for logging traffic that traverses the firewall.
Which log setting is correct?
- A. Enable Log at Session Start
- B. Disable all logging
- C. Enable Log at Session End
- D. Enable Log at both Session Start and End
Answer: C
Explanation:
https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000Clt5CAC
NEW QUESTION # 137
......
Earning the PCNSA certification can be a valuable career move for network security professionals who work with Palo Alto Networks NGFWs. Palo Alto Networks Certified Network Security Administrator certification demonstrates expertise in network security and validates a candidate's ability to protect networks from cyber threats. Additionally, PCNSA certification holders are eligible to pursue advanced certifications, such as the Palo Alto Networks Certified Network Security Engineer (PCNSE) certification.
PCNSA Exam Dumps, PCNSA Practice Test Questions: https://www.trainingdumps.com/PCNSA_exam-valid-dumps.html
Free PCNSA Exam Dumps to Pass Exam Easily: https://drive.google.com/open?id=1ATY3vyoxUFRxNxCFaQU7SvQRNCBkxJ34
